
App Sandbox Runner
Install latest/stable of App Sandbox Runner
Ubuntu 16.04 or later?
Make sure snap support is enabled in your Desktop store.
Install using the command line
sudo snap install app-sandbox-runnerDon't have snapd? Get set up for snaps.
Details for App Sandbox Runner
Package name
- app-sandbox-runner
License
- MIT
Last updated
- Today - latest/stable
Websites
Contact
External link warning
You are about to open
Do you wish to proceed?
Report a Snap Store violation
Report App Sandbox Runner for a Snap Store violation
Snap Store Violation Report submitted successfully
Thank you for your report. Information you provided will help us investigate further.
Error submitting report
There was an error while sending your report. Please try again later.
Share this snap
Generate an embeddable card to be shared on external websites.
Run programs in throw-away sandbox profiles with file-change tracking
App Sandbox Runner is a Linux alternative to Sandboxie-Plus for trying programs and scripts in disposable sandbox profiles and seeing exactly what they changed.
What it really does:
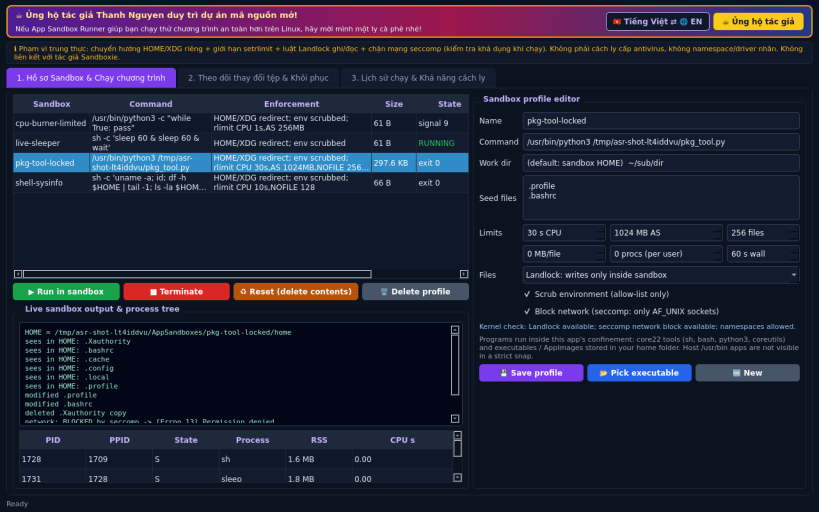
- Sandbox profiles with a private HOME, XDG config/cache/data/state dirs and TMPDIR under ~/AppSandboxes/<profile>, optionally seeded with copies of real-home files
- Scrubbed environment (allow-list) so tokens/secrets in your session do not leak
- Resource limits via setrlimit: CPU seconds, address space (memory), open files, file size, processes, plus a wall-clock timeout that kills the whole process group
- Landlock LSM file rules when the kernel supports them: writes allowed only inside the sandbox folder, optional mode that also hides the real home from reads
- Network block via a seccomp-BPF filter (only AF_UNIX sockets allowed), offered only when the probe shows the filter is really enforced
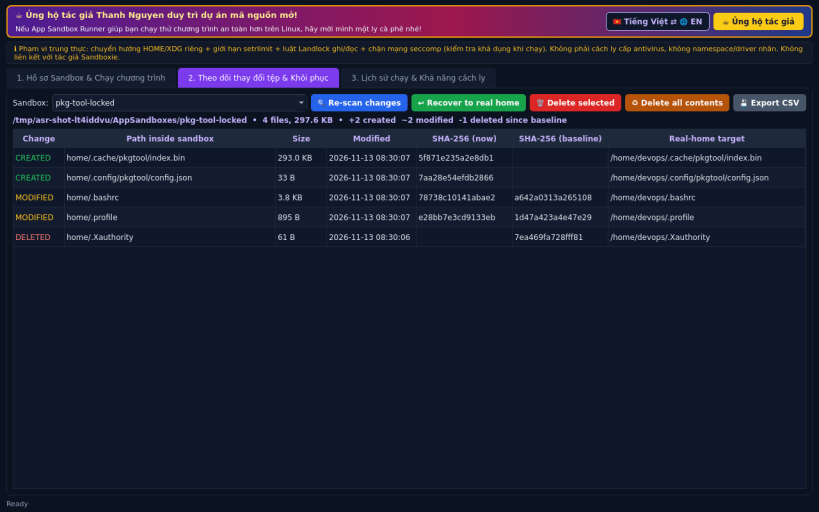
- Full file-change tracking (created / modified / deleted, SHA-256) against the baseline
- Recover a sandbox file to its real-home location (existing file is backed up first), delete selected files or wipe the whole sandbox
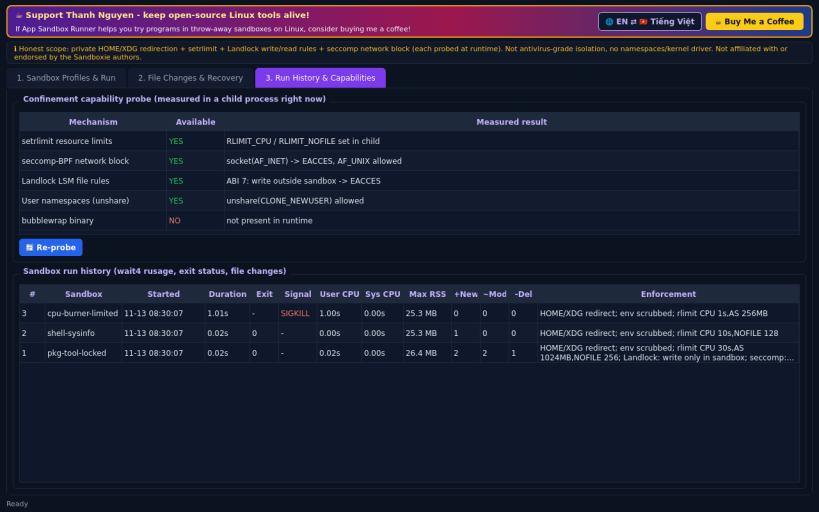
- Run history with exit status / signal, CPU time and peak memory from wait4(), live process tree and output console; capability probe that shows what your kernel allows
Honest limitations: this is NOT antivirus-grade isolation. There are no Linux namespaces (user namespaces and bubblewrap are blocked inside a strict snap), no kernel driver and no virtualisation. In "redirect only" mode a program can still write to absolute paths in your home. X11 programs can still see other X11 windows. Programs run inside this app's confinement (core22 runtime tools and executables / AppImages stored in your home folder). The snap "home" interface does not grant access to hidden files/folders directly in your home (e.g. ~/.bashrc, ~/.config), so such paths cannot be seeded into, or recovered from, a sandbox when installed as a snap.
Disclaimer: This project is an independent open-source tool and is not affiliated with, sponsored by, or endorsed by Sandboxie-Plus, David Xanatos or Sophos.
Support development: https://buymeacoffee.com/thanhnv128b
| Revision | Channel | Version | Build | Commit | Download SBOM |
|---|
The build and commit information is derived from build infrastructure records.
Install App Sandbox Runner on your Linux distribution
Choose your Linux distribution to get detailed installation instructions. If yours is not shown, get more details on the installing snapd documentation.


